Security and data integrity
AI helps. It never bypasses the controls.
The database enforces the accounting rules, tenant isolation and the audit trail, so no one, including the AI, can route around them.
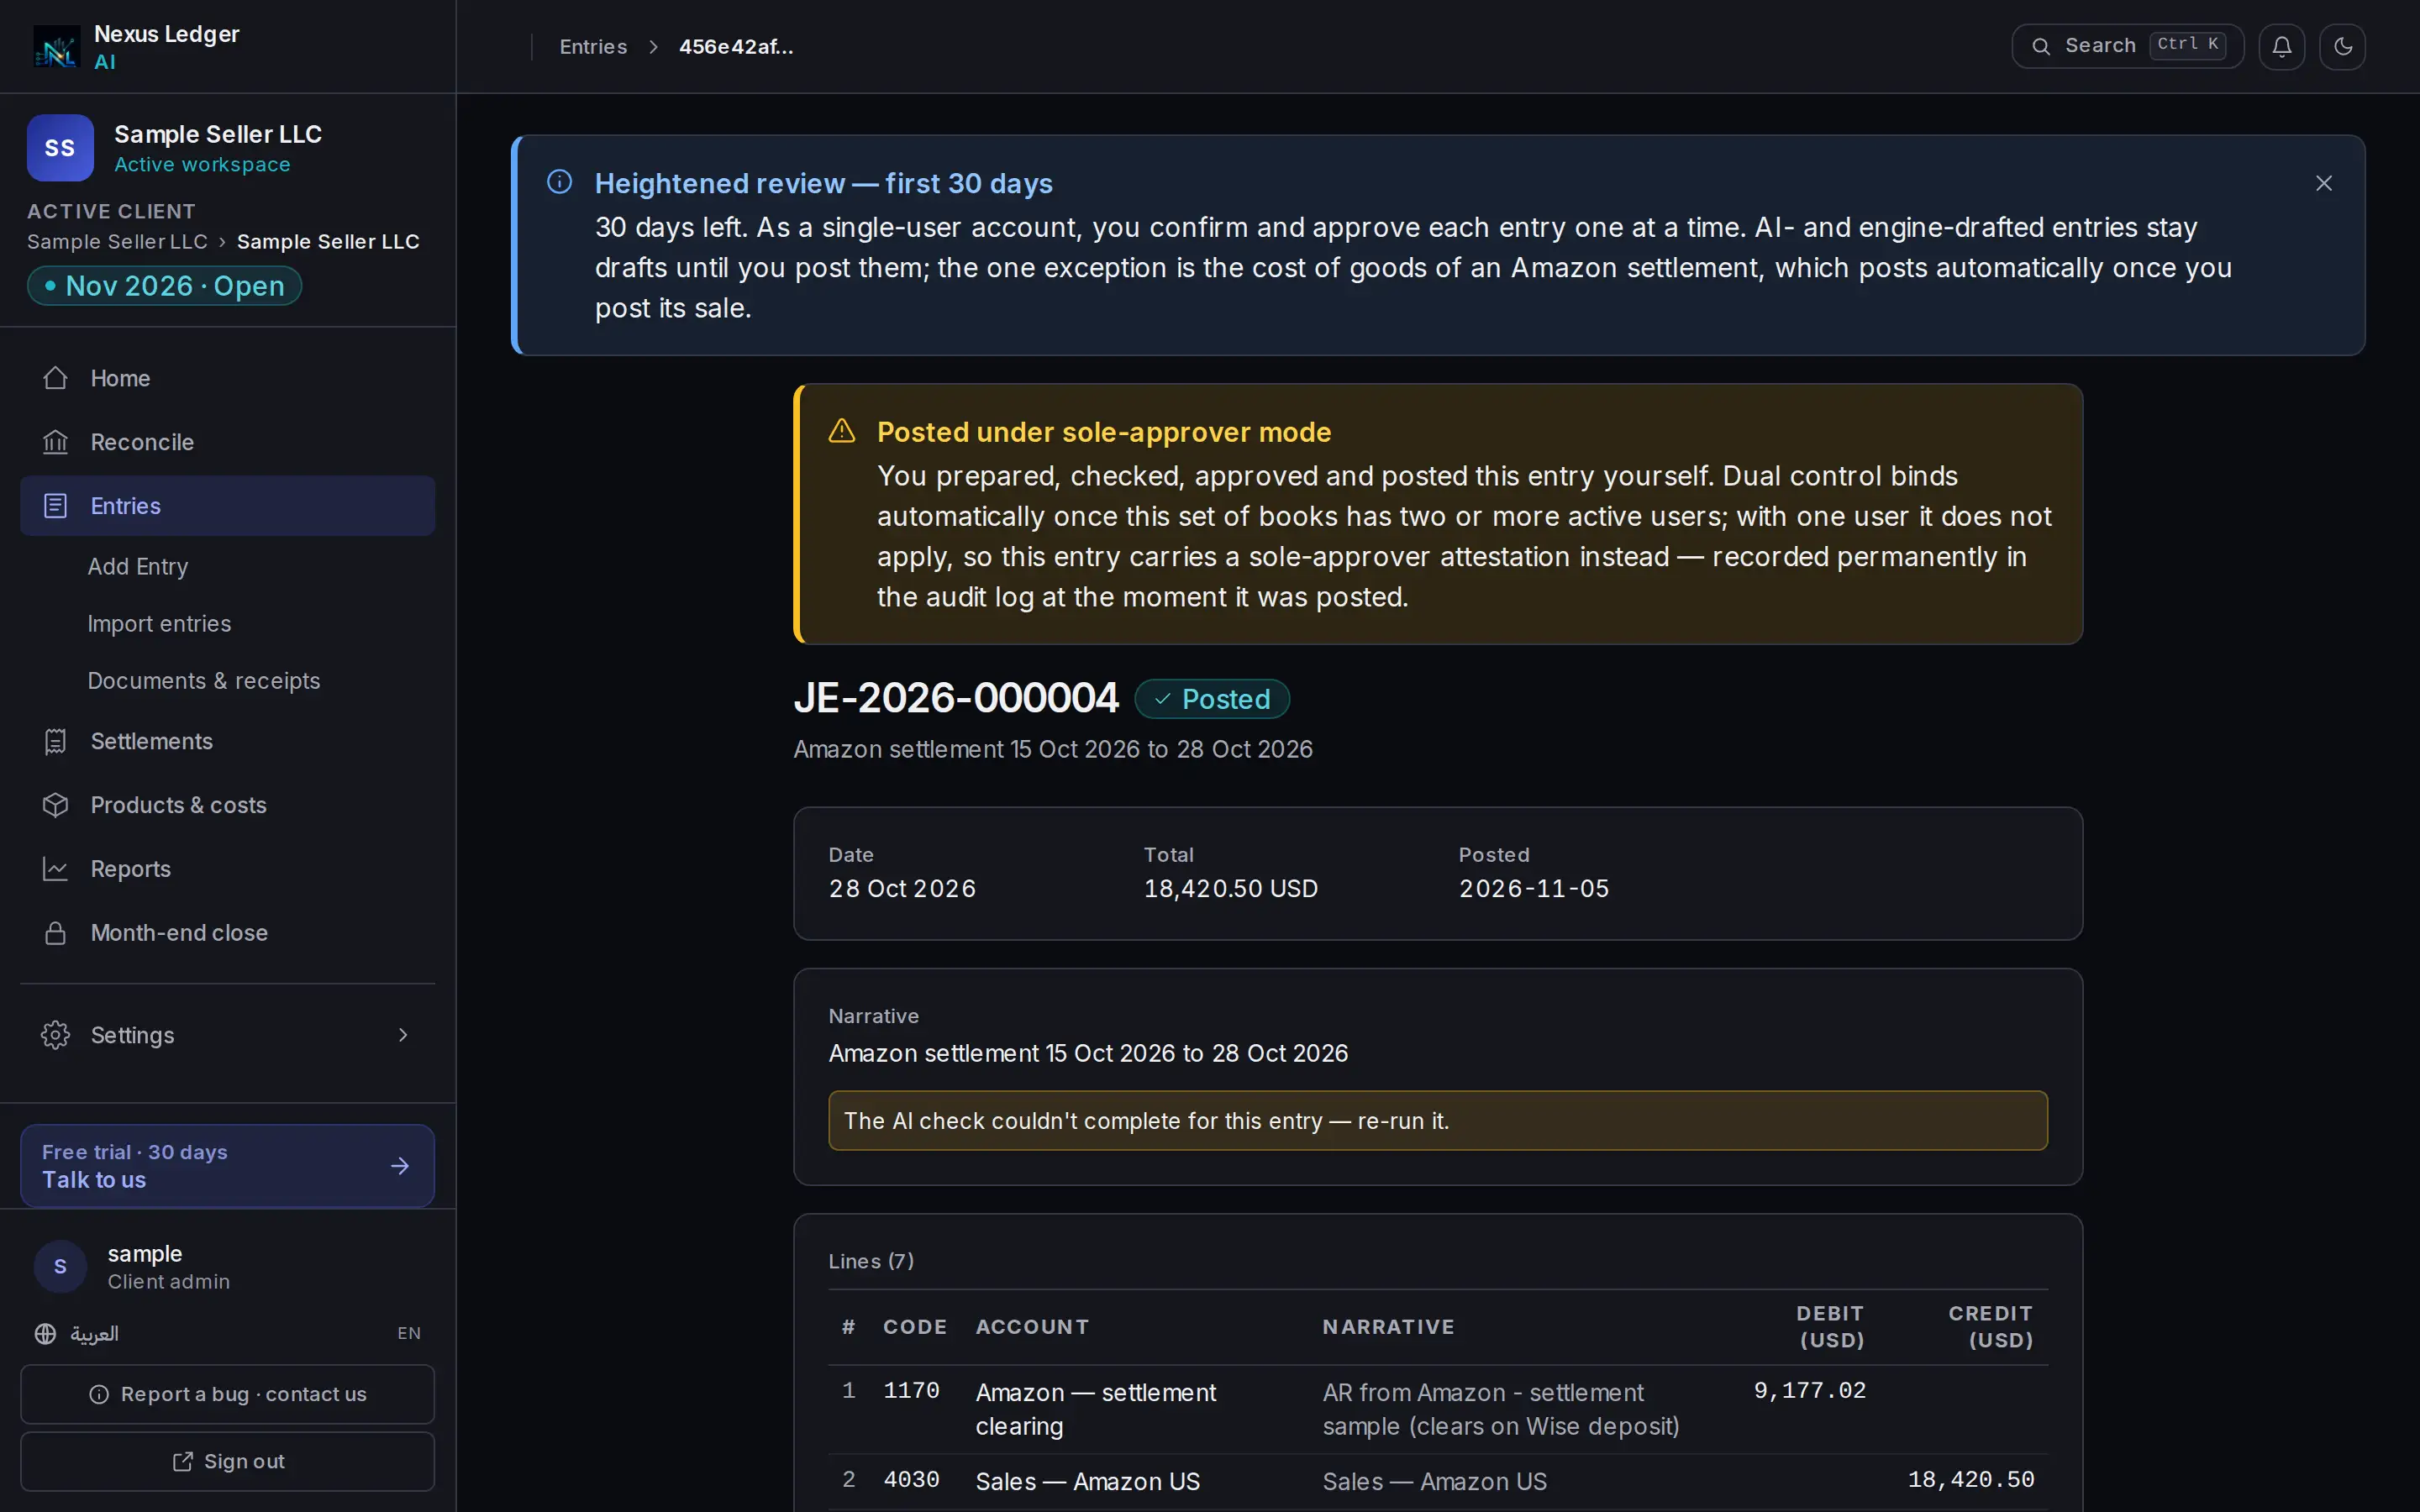
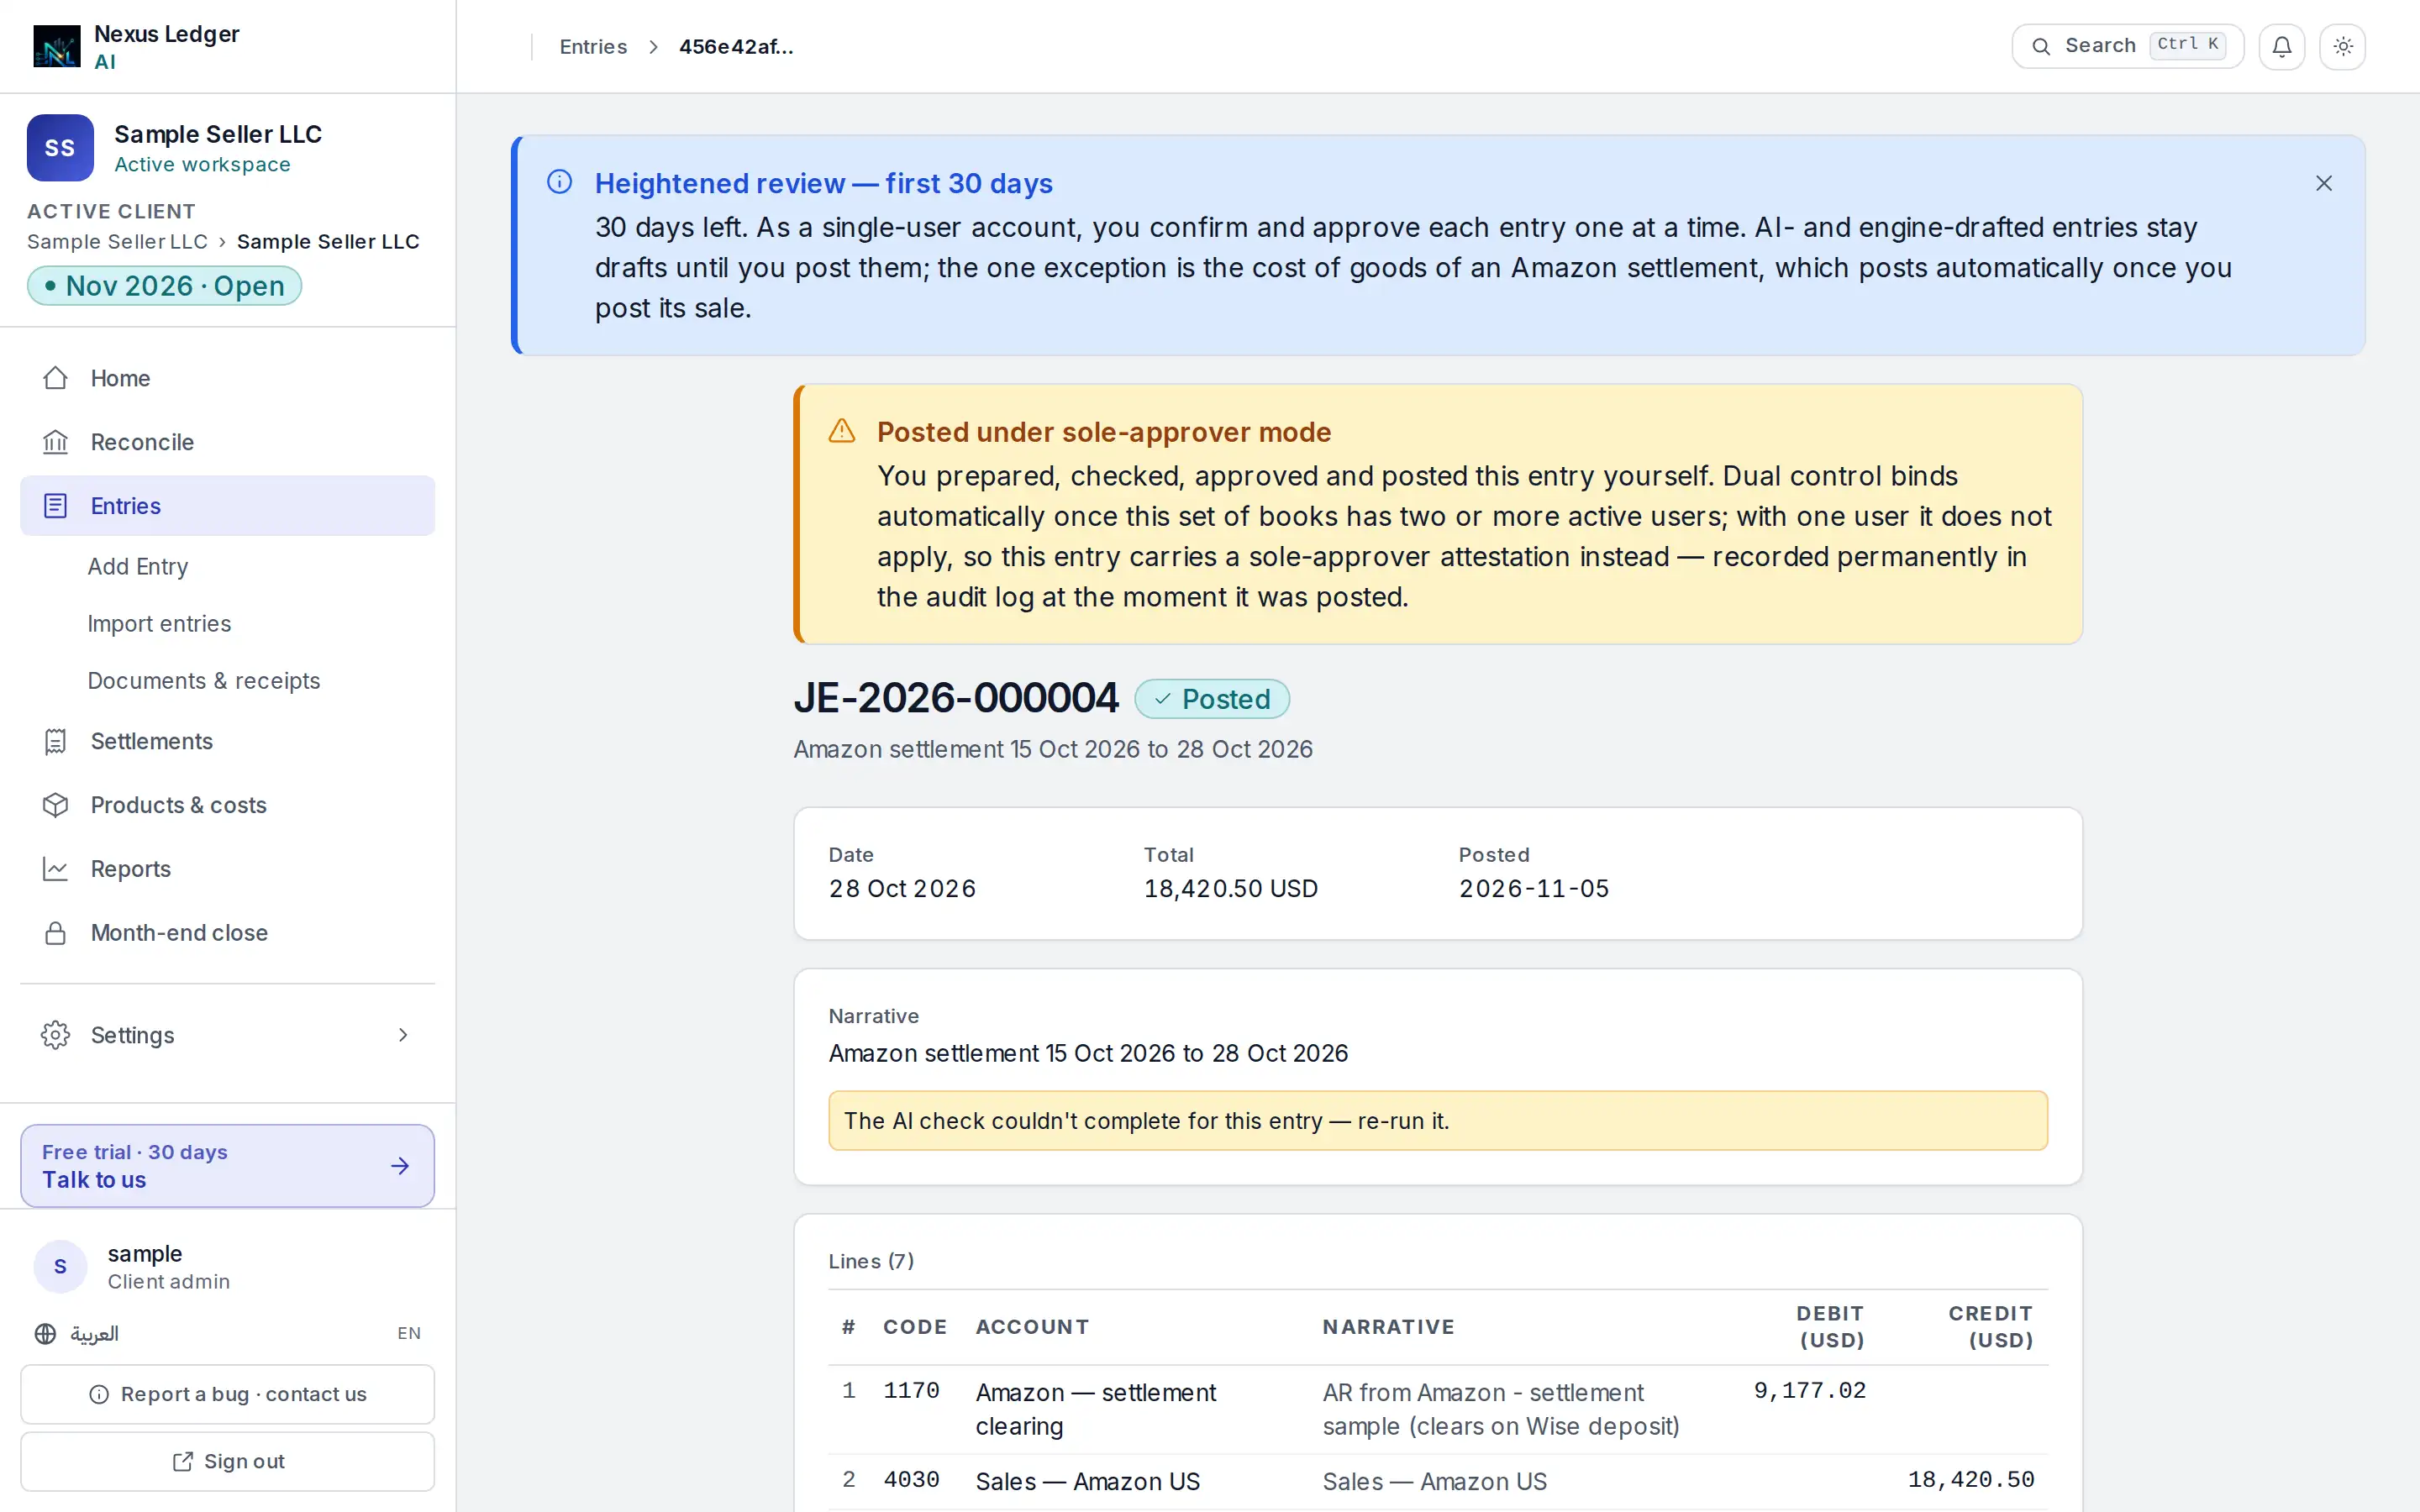
- Sole-approver attestation
- Link to the source
A posted journal entry and its settlement.
Security in four numbers
- Window for the poster to un-post, while nothing downstream has used the entry
- 24 hours
- Audit-logged exception
AI controls
The AI is bound too.
It works through the same permissions as a bookkeeper, and what it drafts stays a draft until a person posts it.
Your documents and settlements
Amazon settlements, bank lines, invoices and receipts.
AI reads, suggests, drafts
Reads uploaded documents, suggests accounts and writes draft entries. Amazon settlements are composed by fixed rules, not by AI.
The database checks
Debits equal credits, the period is open, and the entry belongs to your books.
A draft entry
Nothing is posted yet.
A person posts
You approve, and the entry is locked.
One automatic rule: cost of goods
After you post a settlement's sale, its cost of goods posts by a fixed rule, not by AI, and only while every database check passes. It never touches a bank account, and you can switch it off in Settings.
- A field read with under 85% confidence is held for your review. Under 60%, the document is retried with a stronger model first.
- Text extracted from a document is treated as untrusted data, never as an instruction.
- Every AI call has a token limit, a timeout and a cost ceiling, and a batch cannot exceed its hard cap.
- Your data is not used to train models, by us or by the providers on our subprocessor list.
Control register
What the system guarantees, and how to check it
Each row names the control, what enforces it and where you can verify it. Search this page for any term.
Debits equal credits
How it is enforced
A constraint trigger on journal-entry lines checks that debits equal credits within ±0.0001 when the entry is committed. A write that breaks the rule is rejected, including a server-side one.How you can verify it
In the sandbox, watch a settlement compose into an entry whose difference reads 0.00, then download the composed entry and add the columns yourself. The trigger definition is in the security pack.Check it yourself:Open the sandboxcomposed-entry.csvSample datatrial-balance.csvSample data
Posted entries are locked
How it is enforced
A guard trigger blocks edits to a posted entry and the delete policy refuses it. A correction is a reversal entry linked to the original. One audited exception: the person who posted an entry can un-post it within 24 hours, only while nothing downstream has used it.How you can verify it
Open a posted entry. A reversal carries a badge and a link to its pair.Check it yourself:Open the sandbox
Exactly one automatic post: cost of goods
How it is enforced
After a person posts a settlement's sale, the cost of goods for that settlement posts by a fixed rule, not by AI, and only while every database check passes. The sale, the bank match and every other entry wait for a person. You can switch the rule off in Settings.How you can verify it
In the sandbox, see the cost-of-goods entry that follows a posted sale. In the app, its audit row names the rule and records no approver.Check it yourself:Open the sandbox
Who approved it
How it is enforced
Dual control applies from two active users: the checker and the approver cannot be the preparer. A single-user account approves as sole approver, and every such post writes a permanent attestation to the audit log.How you can verify it
Open a posted entry. The attestation appears on it, in English and Arabic.Amazon access is Finance and Accounting only
How it is enforced
The connection asks Amazon for one role, Finance and Accounting, and nothing else. It cannot read inventory, advertising or buyer personal data, because the access we are approved for does not include them.How you can verify it
Open the connect step in the capture below to see what you grant. You can review or withdraw the authorisation in your Amazon seller account at any time.Check it yourself:See the connect stepsample-settlement.txtSample data
Sign-in and multi-factor
How it is enforced
Sign in with email and password, or with an emailed sign-in link. Admin roles must enrol an authenticator app (TOTP) before their per-role enforcement window lapses; after that, admin pages redirect to enrolment. Sensitive pages already require a stepped-up, MFA-verified session for enrolled administrators. A stricter default window and database-boundary enforcement are staged rollouts.How you can verify it
Open the account security page to enrol or review your authenticator.Check it yourself:See the security page
Tenant isolation
How it is enforced
Row-level security is enabled on every business table and keys on both your account and your books. Triggers reject a reference to another tenant's row before it commits.How you can verify it
Request the policy listing from the security pack.Append-only audit log
How it is enforced
Every workflow transition writes a row with the actor, the time and the previous and new state. Application roles can read the log; there is no insert, update or delete path from a user session. Rows are designed to be kept for 11 years.How you can verify it
Open the audit log in the app, or any posted entry's history.Source documents stay private
How it is enforced
Uploaded documents are held in private storage. Opening one makes the server re-check your tenant scope and issue a signed link that expires after 10 minutes.How you can verify it
Open a source document from an entry, then reuse the link after 10 minutes.Hosted in the EU
How it is enforced
The database and document storage run in Stockholm, Sweden. The extraction worker runs elsewhere in the EU. There is one production region.How you can verify it
Every processor, what it does and where, is on the subprocessor list.Check it yourself:Subprocessor list
No bypass key in the browser
How it is enforced
The database key that bypasses row-level security exists only in server environments. It is never in client code, committed workflow files or prompts.How you can verify it
Inspect the page's JavaScript. It contains no such key.Encryption
How it is enforced
Provider-managed: our database and storage providers encrypt data at rest with AES-256, and traffic uses TLS 1.2 or later, with HSTS on the public domain.How you can verify it
Check the provider documentation, or inspect the TLS certificate and the HSTS header.Signed callbacks
How it is enforced
Billing, extraction-worker and OAuth callbacks verify signatures before they are processed. Each is keyed by event id and payload hash, so a replay does nothing.How you can verify it
Request the callback handling notes from the security pack.Our access to your books
How it is enforced
There is no log-in-as-customer path. Read-only incident access needs a written admin grant, expires after 24 hours and is audit-logged.How you can verify it
The access-grant policy is in the security pack.
See it
The two screens behind the claims
Real captures of the product on sample data, not mock-ups.
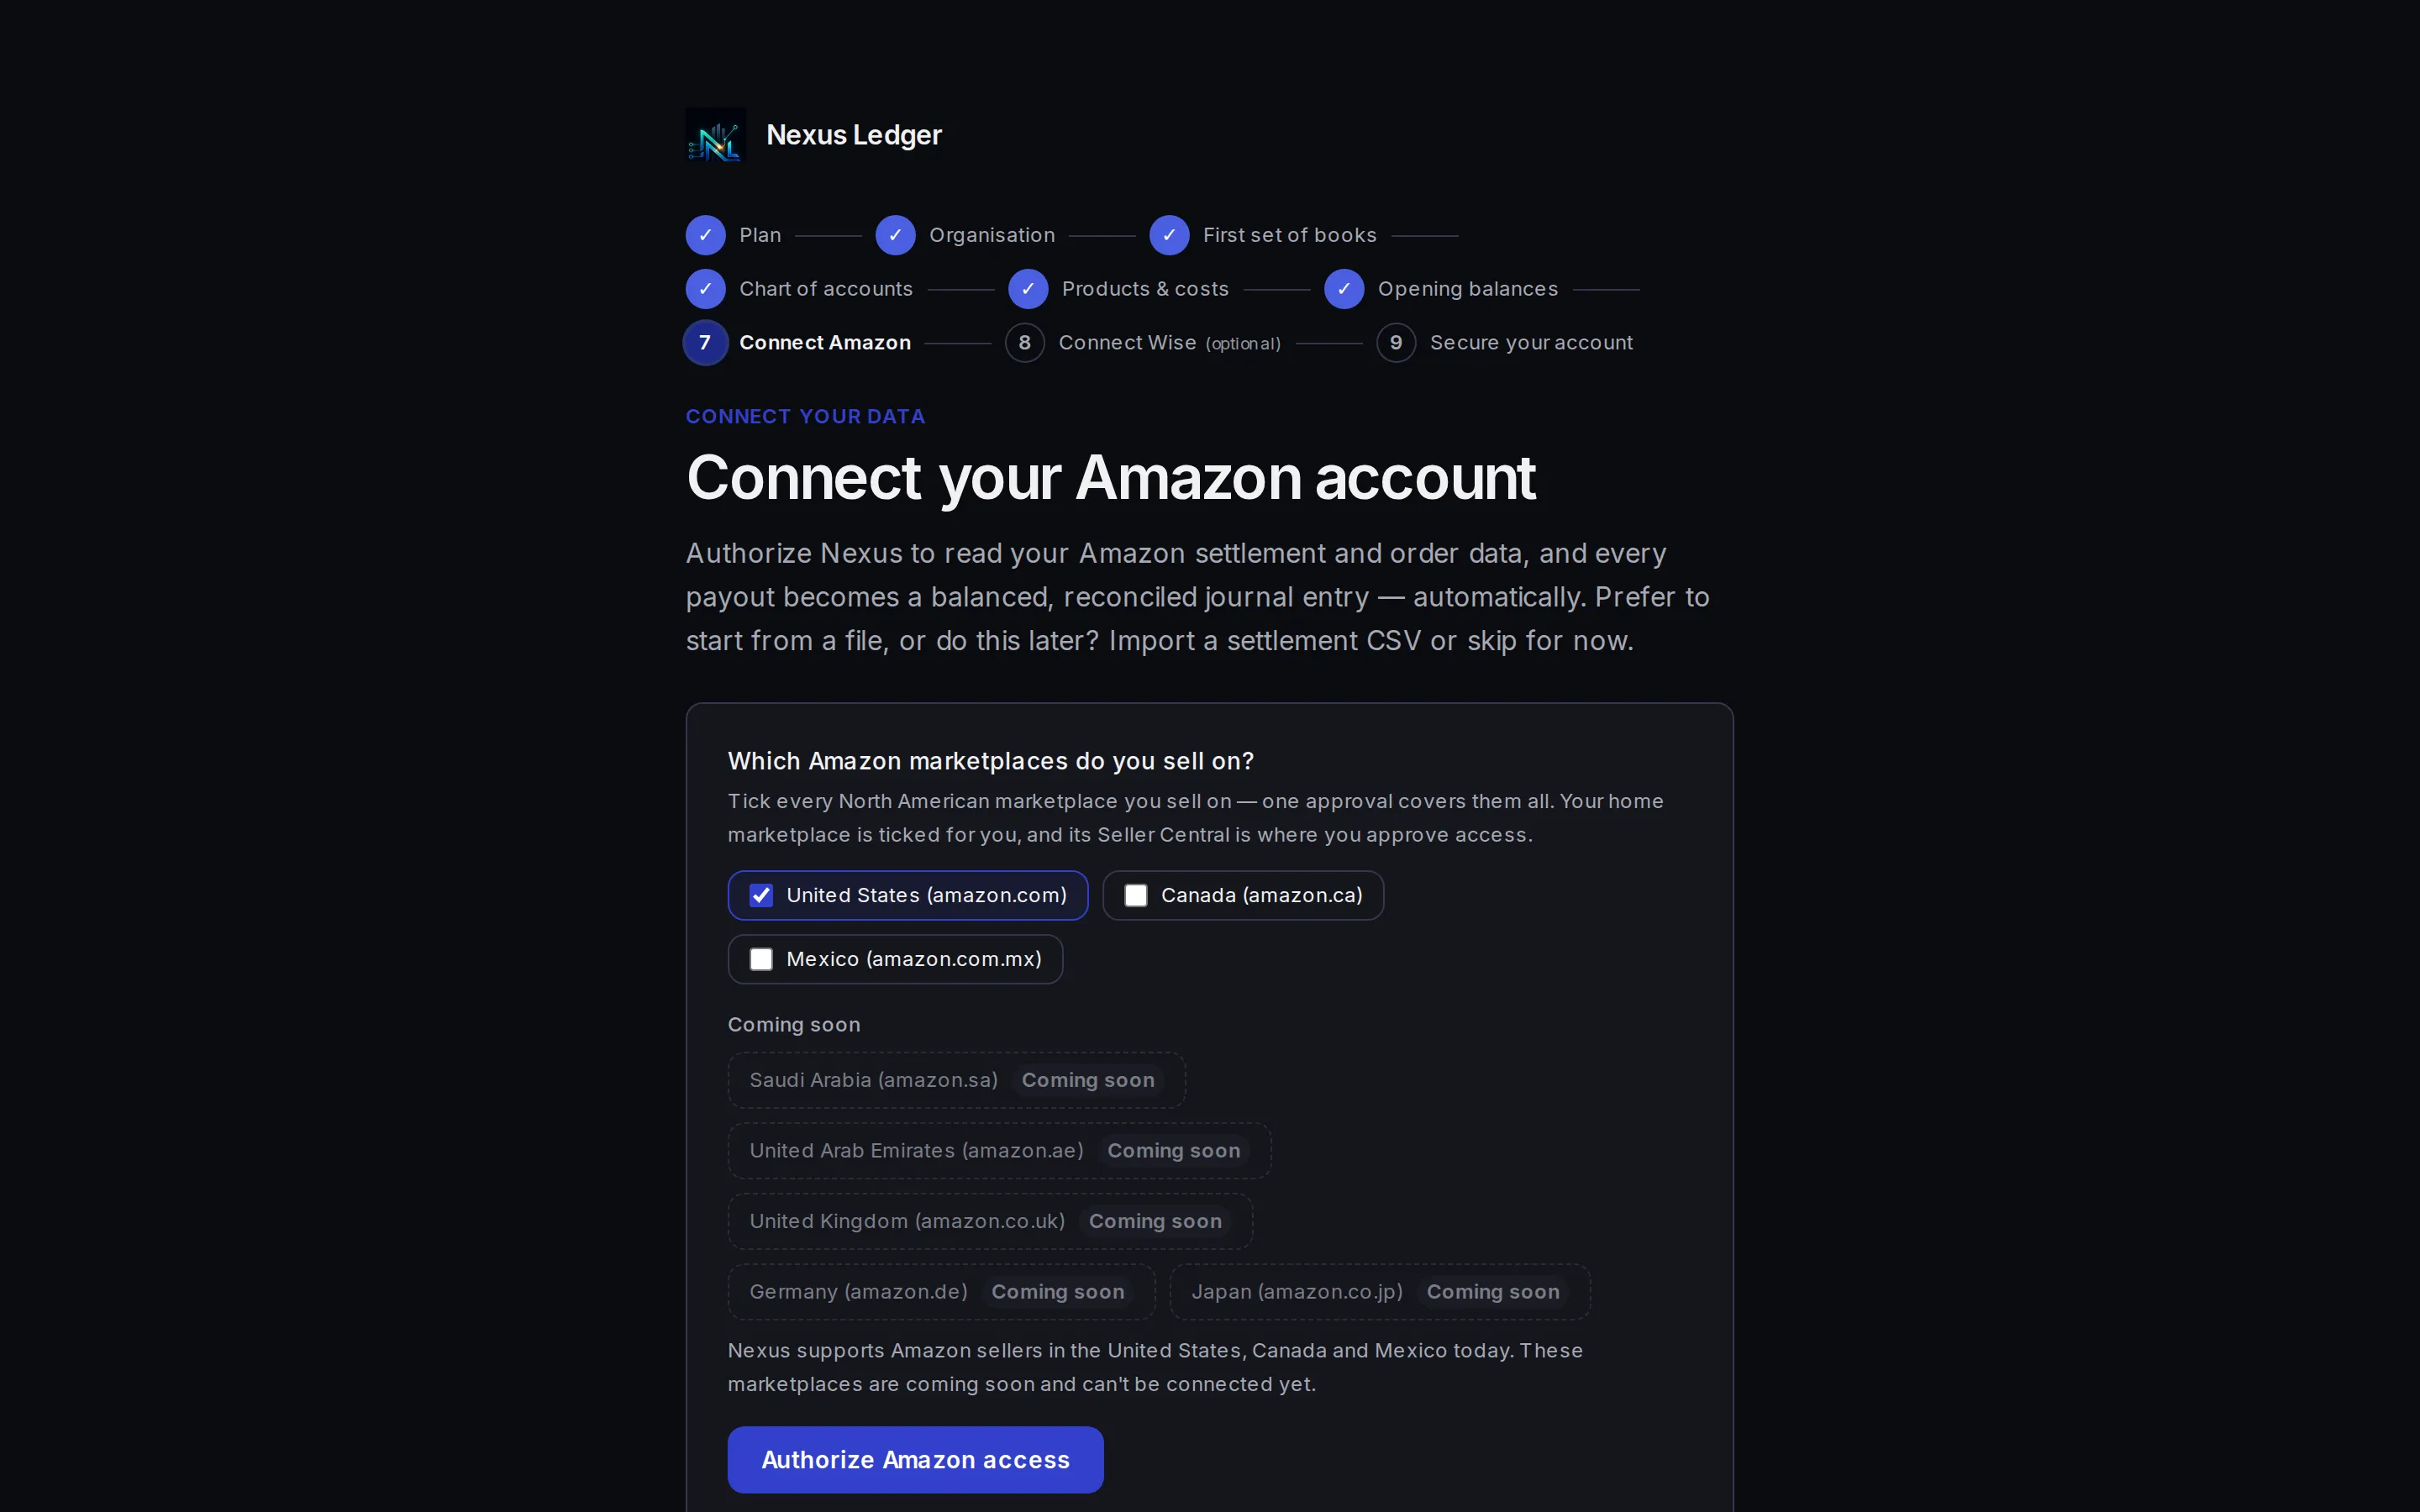
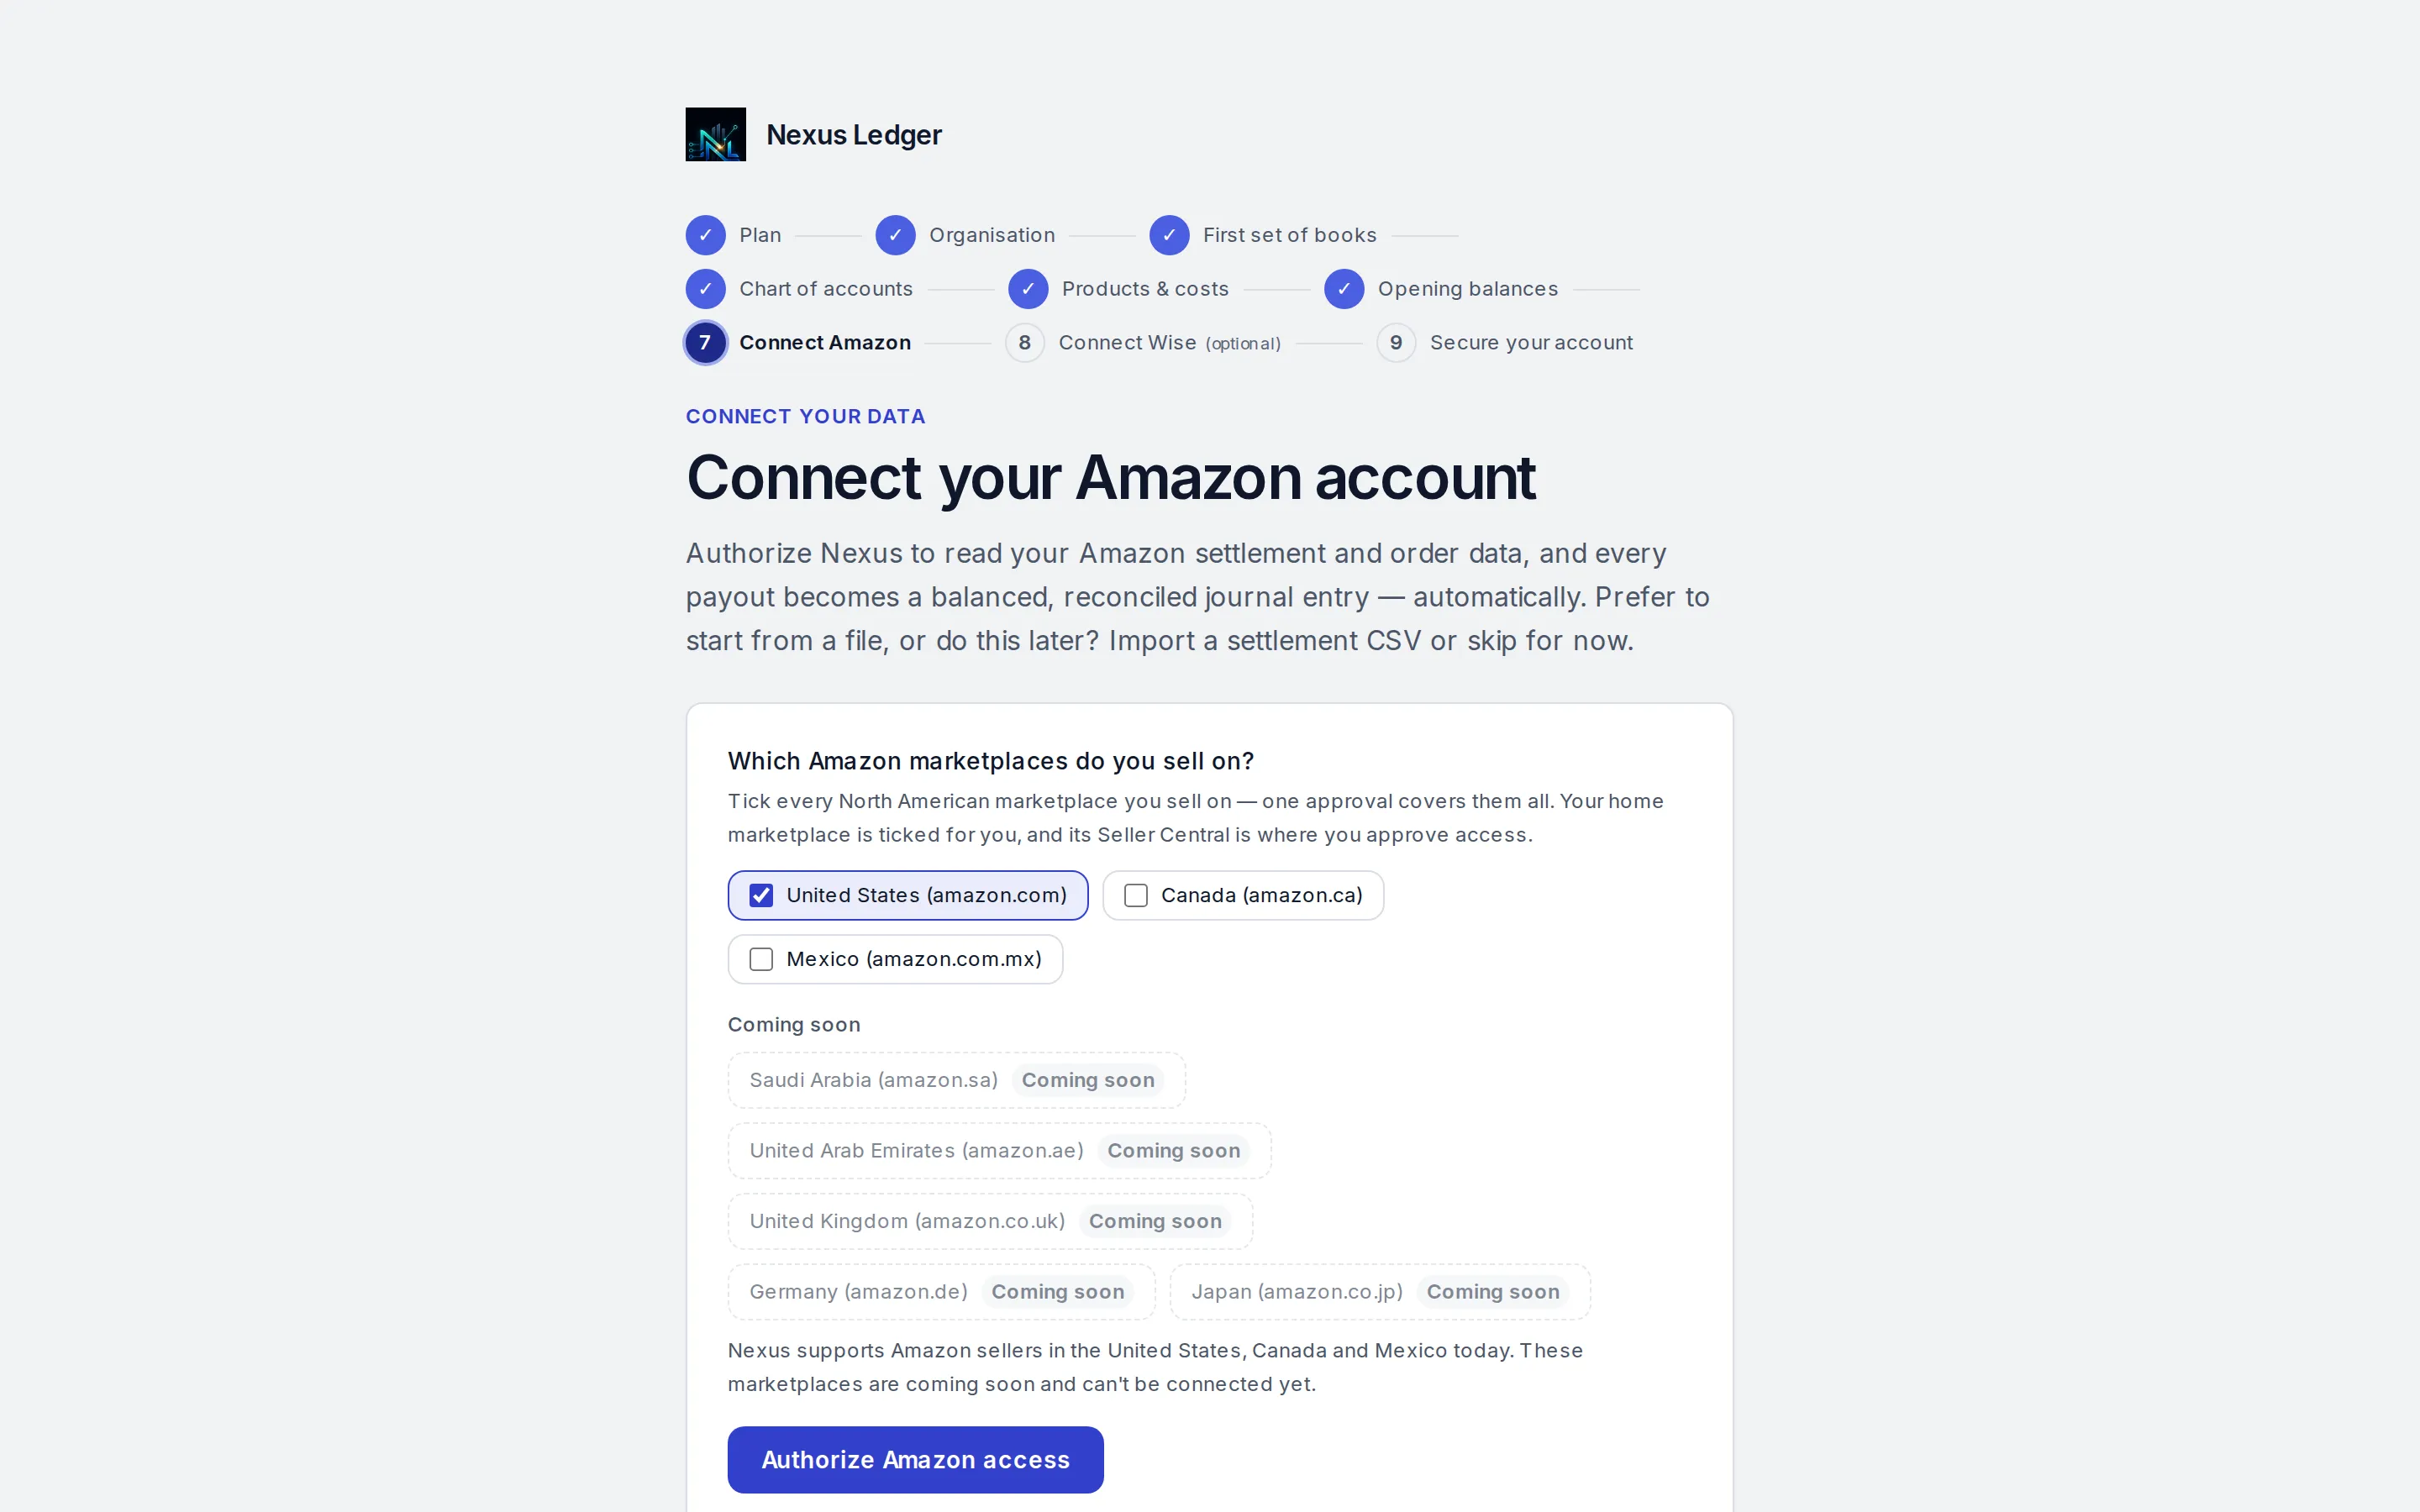
Amazon access: Finance and Accounting only
The access you grant is the Finance and Accounting role. Nothing else is requested.
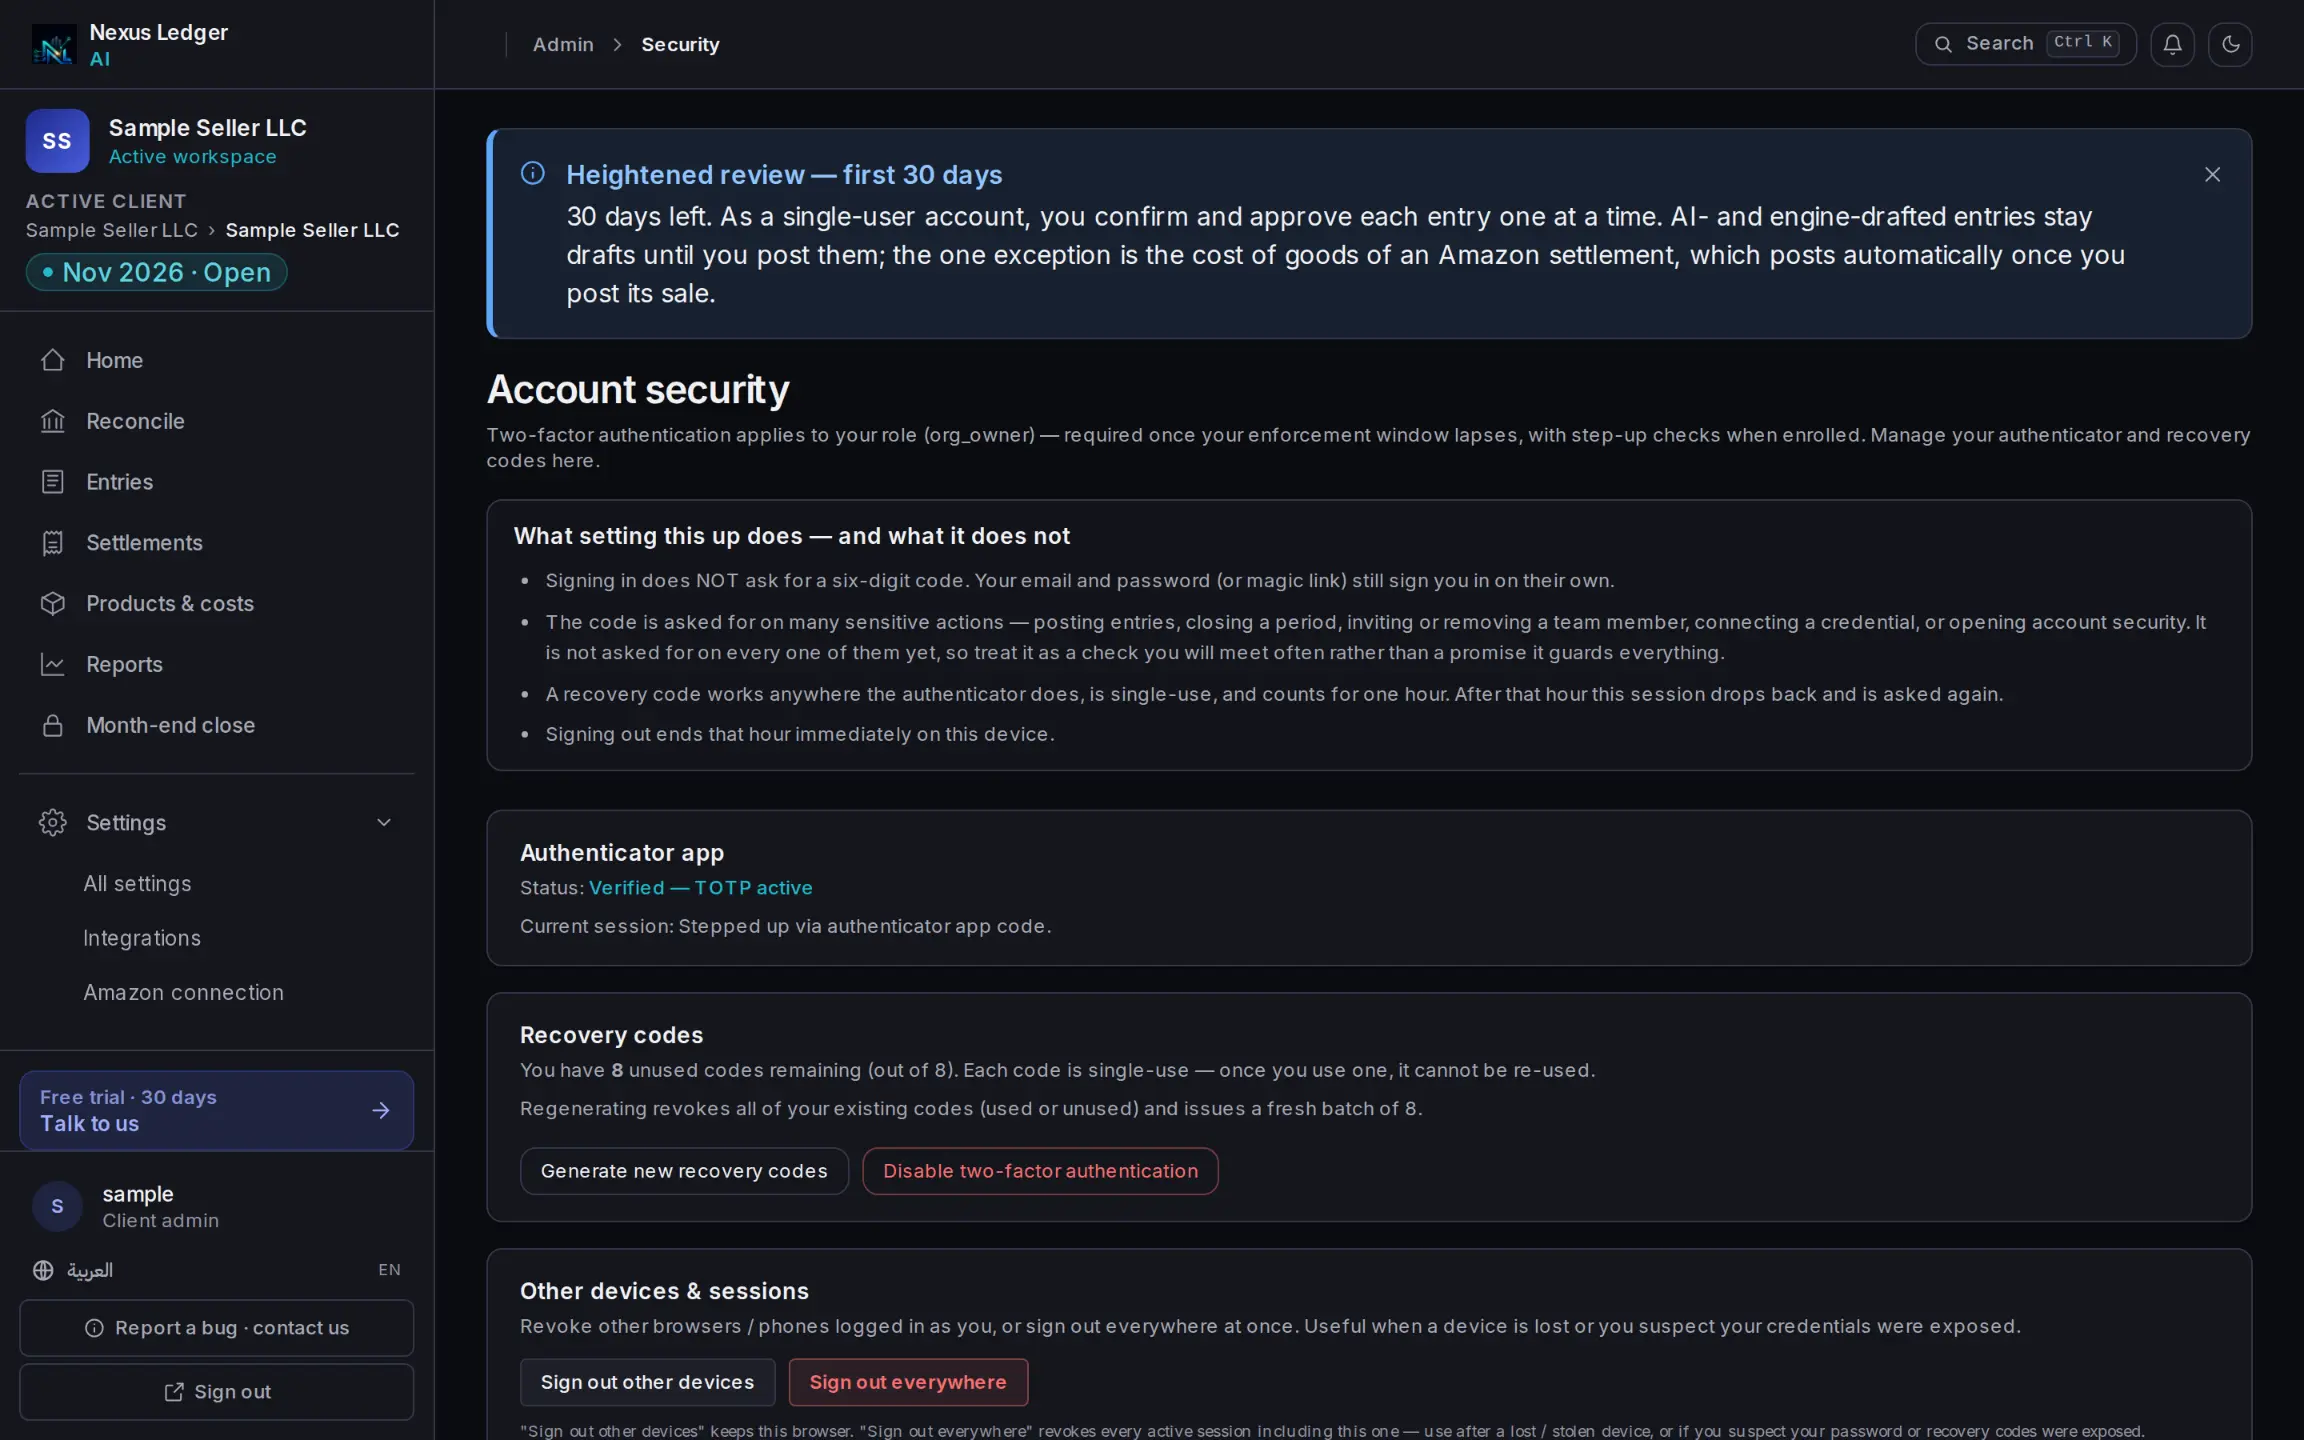
Sign-in with multi-factor
Admins enrol an authenticator app here. Sensitive pages ask for a stepped-up code once you are enrolled.
Hosting and compliance
Where your data lives
One production region, named plainly.
- Hosted in the EU
- The database and document storage run in Stockholm, Sweden. The extraction worker runs elsewhere in the EU. There is one production region.
- Backups
- The managed database platform runs automated, encrypted backups. Off-region backup copies, document-bucket replication and quarterly restore drills are part of the general-availability hardening plan, stated here as the plan and not yet a certified current control.
- Certifications
- SOC 2 and ISO 27001 are targeted, not held. We show no certification badge.
- Processors and your rights
- Every processor, what it does and where, is listed in full on the subprocessor page. Your rights are in the privacy policy. A Data Processing Addendum is available on request.
Security pack for procurement
The data-processing addendum, the subprocessor list, the control descriptions and answers to your security questionnaire, in one request.
Questions procurement asks
Straight answers
- Do you train AI models on our data?
- No. We do not opt customer extractions or chat history into any model-training pipeline, and our agreements with the providers on the subprocessor list prohibit training on Customer Data. Anonymised, aggregated counts (pages, entries, document-type mix) may inform product improvement; the underlying content never does.
- Can one customer see another customer's data?
- No. Row-level security is enabled on every business table and keys on both the account and the books. Triggers reject any cross-tenant reference before it commits, and the key that bypasses these policies never reaches the browser.
- Can a posted journal entry be edited or deleted?
- No. A guard trigger blocks edits and the delete policy refuses; corrections are reversal entries linked to the original. The one narrow exception is a 24-hour un-post by the person who posted it, only while nothing downstream has used the entry, and it is itself audit-logged.
- Where is our data hosted?
- In the EU: the database and document storage in Stockholm and the extraction worker elsewhere in the EU, on every plan. There is one production region.
- Can you see our books?
- Not routinely. There is no log-in-as-customer path. Read-only access to one tenant needs a written admin grant, expires after 24 hours and is audit-logged.
- Do you hold SOC 2 or ISO 27001?
- Not yet. Both are targeted. The controls on this page already exist, so a certification would formalise them rather than build them.